

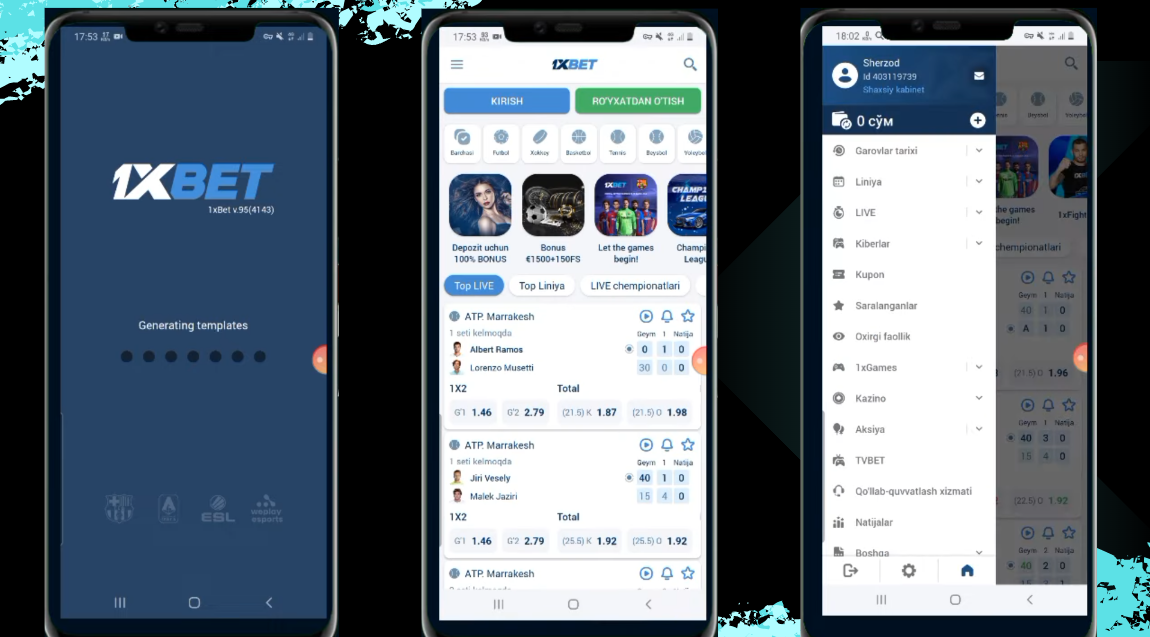
A fresh phone in your hand means a clean slate for whatever software you choose to load. The 1xBet application for Android arrives as an APK package rather than through the Play Store, which changes how the screens present themselves during acquisition and setup. You will encounter system dialogs that other gambling apps never trigger, each demanding a conscious security decision. Understanding what those prompts actually request prevents hesitation halfway through the process.
Preparing the Device Before Any Download Begins
Android’s default configuration blocks software from outside Google’s ecosystem. This protection layer remains invisible until you attempt something the operating system considers non-standard. Several elements warrant verification before the browser touches any external server.
- Open the storage settings and confirm several hundred megabytes remain free; compressed APKs expand during unpacking.
- Update your current browser to the newest available build; rendering engines from two years ago sometimes mishandle modern download redirects.
- Locate your existing 1xBet account credentials or prepare to register fresh, since the app demands authentication before displaying any betting markets.
- Charge beyond fifty percent; installation routines abort if the system triggers battery preservation mode mid-process.
- Note whether your phone recently received an Android version upgrade, as permission structures changed significantly after Android 10.
A stable Wi-Fi connection reduces corruption risk for packages exceeding typical app dimensions. The operating system maintains download caches silently; clearing older temporary files beforehand prevents filename collisions that confuse the installer.
Obtaining the Package and What the Browser Requests
The acquisition phase presents two distinct visual states depending on your navigation choices. Mobile sites typically detect Android user-agents automatically and surface download triggers without manual searching.
Finding the 1xbet android package android version triggers a standard browser download overlay. Chrome and its derivatives display a bottom-sheet confirmation with the filename, file category marked as “unknown,” and a discrete save location. Edge and Firefox variants surface similar information through top-bar notifications. The critical observation: none of these browsers explain what “unknown” categorization implies for subsequent installation steps.

During the transfer, the screen shows a progress indicator without percentage detail. Large packages may appear to stall; the operating system pauses background transfers when thermal throttling activates. Interrupting this phase corrupts the package irretrievably, forcing a fresh retrieval. The browser aggregates completed downloads in a single list accessible through its menu; the APK sits there awaiting your explicit tap to launch installation.

Installation Dialogs and Permission Architecture
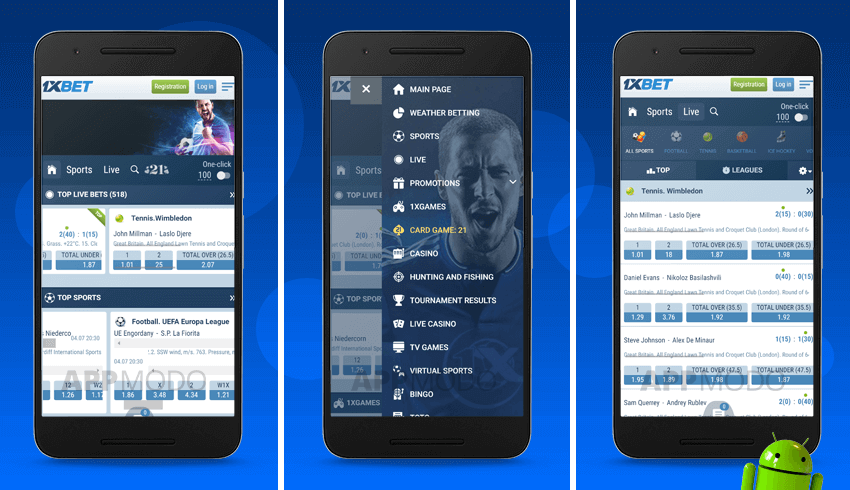
Tap the downloaded item and the interface shifts immediately to Android’s package installer. The first screen presents application permissions grouped by category: location access, storage modification, network state inspection, and others. Each toggle expands to reveal sub-behaviours. This differs fundamentally from Play Store presentations where permissions appear as scrolling text; here, active selection is required.
The blocker appears on the subsequent screen. A full-screen overlay states the system cannot install from this source, with two buttons offering contradictory paths. “Cancel” returns you to the browser. “Settings” transports you to a granular permissions panel titled something like “Install unknown apps” or “Apps from this source.” The modern Android approach assigns permission per originating application rather than globally. Your browser, your file manager, and your messaging apps maintain independent toggles.
| Screen Element | What It Actually Controls | Recommended Response |
|---|---|---|
| Browser toggle in Settings | Whether that specific browser may trigger installers | Enable temporarily, disable post-installation |
| “Allow from this source” checkbox | One-time authorization for current session | Verify package hash if source is unfamiliar |
| Google Play Protect warning | Heuristic scan of package signatures | Review details, proceed if checksum matches |
| App-level permission prompts | Runtime requests after first launch | Grant location only if live betting geofencing required |
Return to the installer after enabling the toggle. The screen sequence repeats, now presenting an “Install” button instead of the previous blockage. A secondary progress bar fills as the system unpacks resources, creates the application directory, and registers components with the package manager. Completion displays “Open” and “Done” simultaneously; selecting “Done” preserves the installation flow without immediate launch.
Maintaining Current Versions and Functional Alternatives
Update mechanics mirror the original acquisition. The installed application detects server-side version mismatches and surfaces in-app banners. Tapping these relaunches the browser-to-installer sequence identically. Crucially, Android rejects updates signed by certificates differing from the original installation. This cryptographic mismatch presents as a generic “App not installed” dialog without explanatory detail. The resolution requires complete removal and fresh installation, which destroys locally stored credentials, cached betting histories, and cricket coverage match reminders unless cloud synchronization was previously enabled.
The mobile website operates through responsive design rather than native code. Browser-based access circumvents all permission complications but sacrifices push notification immediacy for live odds movement. Geolocation requests still appear, now wrapped in the browser’s own permission framework instead of Android’s system layer. Session persistence depends on cookie acceptance and local storage availability; aggressive browser privacy modes break this continuity.
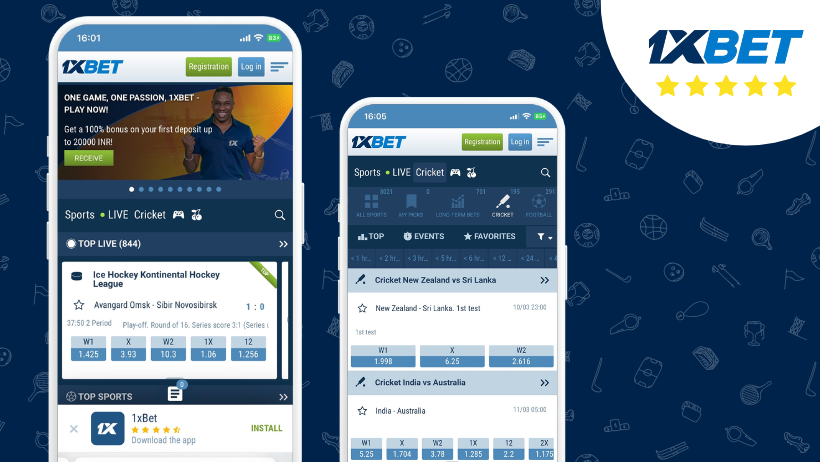
Core functionality spans identical territory regardless of interface choice. Pre-match wagering across conventional and esports categories, live proposition markets updating in sub-minute intervals, slot and table game libraries, and account funding through regionally varied payment rails. The application bundles these with biometric login options and gesture-based bet-slip composition that browser implementations cannot replicate. Set deposit limits through the responsible gambling panel before engaging any wagering functionality; this setting propagates across both application and web sessions.
Installation Failure Patterns and Resolution Paths
Several predictable stalls surface repeatedly during support inquiries. The “Parse error” indication almost always signals incomplete download—corrupted segments from interrupted transfers. Delete the partial file entirely and reacquire rather than attempting resumption. “Blocked by Play Protect” overlays emerge from Google’s real-time scanning; the secondary “Install anyway” button remains available after tapping through the warning details.
Storage-related failures manifest differently across Android generations. Older releases complain of “insufficient storage” with byte-level estimates. Contemporary versions silently fail, returning users to the app drawer without explanation. Check available space through Settings > Storage, remembering that installation requires working headroom beyond the final installed size. Package manager conflicts arise when modified applications remain installed; the system refuses to overwrite without explicit uninstallation first, presenting this as an unnumbered error dialog with technical package names.
FAQ
Why does the screen ask for “unknown sources” permission specifically for my browser?
Android evolved from global installation permissions to per-source authorization. Your browser initiated the download, so Android attributes installation risk to that application. Enabling the toggle grants only that browser temporary installation rights; other applications remain restricted.
What does the “signature verification failed” screen indicate during updates?
The incoming package carries a digital certificate mismatching your installed version. This prevents malicious interception but breaks legitimate update paths when publishers rotate signing keys. Uninstall completely and reinstall fresh, accepting data loss.
Why does the location permission screen appear immediately after first launch?
Live betting functionality requires geolocation confirmation in many jurisdictions. The app requests this at runtime rather than during installation. Denial restricts certain market categories without preventing general account access.
What triggers the “Download blocked” screen in some browsers?
Safe browsing databases flag gambling-related APK distribution domains. The browser requests explicit confirmation that you understand this classification. This differs from malware warnings; proceed only if you independently verified the source authenticity.
Why does the app request screen overlay permission after installation?
Floating odds tickers and live-match mini-windows require drawing over other applications. Granting this enables multitasking during live events. Denial confines betting activity to full-screen app sessions without background information display.